DATA SECURITY

Data Access Governance

Automate access requests, review entitlements, and enforce ethical walls. Every request stays on record.

Book a demo
Free risk assessment

Trusted by 8,000+ customers

OVERVIEW

IT can't know who should have access.Your data owners can.

Varonis routes every access request to the person who owns the data. Approved changes are applied for you, and every decision is kept on record.

Self-service requests

Your users request access to folders, sites, and groups from one portal. Each request goes straight to the right owner.

Your users request access to folders, sites, and groups from one portal. Each request goes straight to the right owner.

Multi-level approvals

Add authorizers at as many levels as you need. Each level approves before the next one sees the request.

Add authorizers at as many levels as you need. Each level approves before the next one sees the request.

Changes applied for you

Once a request is approved, Varonis commits the change to your data source. No tickets for IT.

Once a request is approved, Varonis commits the change to your data source. No tickets for IT.

Reduce your blast radius

Focus on the permissions and exposed data that could increase the impact of a breach.

Accelerate compliance

Bring data discovery, access visibility, and activity monitoring together to support your compliance program.

OWNERSHIP

Give data owners control

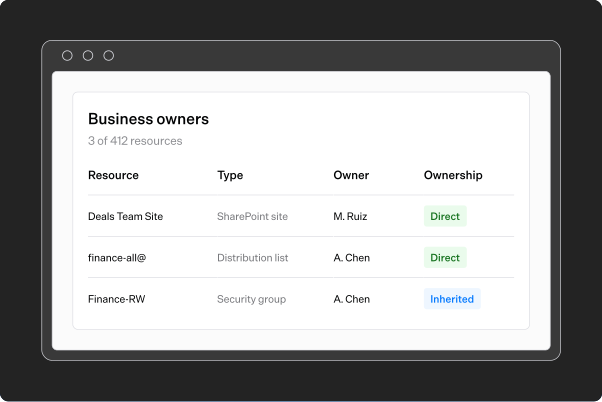
Assign a business owner to each share, site, or group. Ownership flows down to every folder below it. Owners see only their own resources and requests.

Business-owner assignments for data resources, showing direct and inherited ownership
Varonis product overview
auto
image

REQUESTS

Approve access with a click

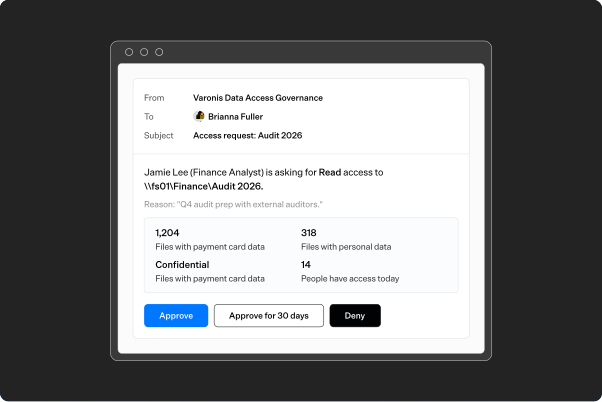
Your users request access for themselves or someone else. Owners and authorizers approve or deny it. Varonis applies the change. Requests left pending for 30 days cancel on their own.

Approve access request dialog
Varonis product overview
auto
image

ATTESTATIONS

Automate entitlement reviews

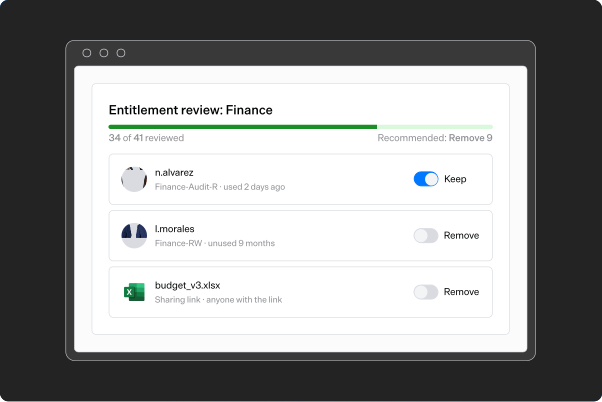
Owners recertify access on a schedule. Keep what's needed and remove what isn't, including file-level sharing links. Each review covers only the owner's data.

Scheduled entitlement review
Varonis product overview
auto
image

Ethical walls

Enforce ethical walls

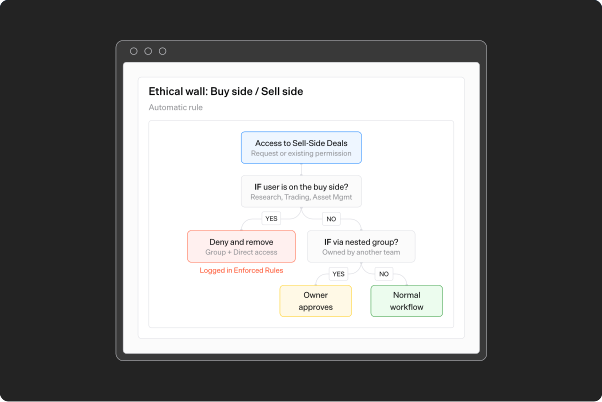
Block all access between teams that must stay apart, like your buy-side and sell-side teams. Automatic rules remove access by group membership or direct permission. The Enforced Rules report shows every action.

Ethical wall access enforcement workflow
Varonis product overview
auto
image

FAQs

Common questions

Which data sources does it support?

Windows file shares, Active Directory, Entra ID, and Microsoft 365, including SharePoint Online, OneDrive, and Teams. Linux, IBM AIX, and other CIFS sources work with extra packages. Exchange Online isn't supported.

Which group types can it manage?

Entra ID security groups, Microsoft 365 groups, mail-enabled security groups, SharePoint groups, Windows local groups, and AD distribution groups. Azure distribution lists aren't supported.

How fast do changes take effect?

Group changes sync within 30 minutes. So do changes made through the API. Direct permission changes apply on the next scan, usually within 25 minutes to 4 hours.

Can it govern individual files?

No. It governs containers like sites, libraries, and folders. You can still remove file-level sharing links during a review.

How long are requests kept?

Indefinitely. Every membership, permission, and review request stays searchable and reportable.

Does it work across domains?

Yes. It supports one-way and two-way domain trusts. Cross-domain requests follow your trust settings.

Is it FedRAMP authorized?

Yes. Data Access Governance is FedRAMP Moderate.

Ready to see Varonis in action?

Schedule a demo
https://cdn.prod.website-files.com/6aad3cd63e81c645c771a0be/6aad48e61926ad27c8821c7b_varonis-conversion-blue.mp4
https://www.youtube-nocookie.com/embed/717uPD8k5nc