


One policy for every agent
Cursor, Claude Code, GitHub Copilot, and more. Your policy stays the same when developers switch tools.
Cursor, Claude Code, GitHub Copilot, and more. Your policy stays the same when developers switch tools.
AI SECURITY
Varonis Atlas secures the coding agents your developers use. Block risky commands, catch agents that drift from the task, and find malicious skills in your repos.
Trusted by 8,000+ customers




OVERVIEW
A developer asks for a small change. The agent picks its own files, commands, and MCP servers. Atlas checks each action against the task and your policy before it runs.
Cursor, Claude Code, GitHub Copilot, and more. Your policy stays the same when developers switch tools.
Cursor, Claude Code, GitHub Copilot, and more. Your policy stays the same when developers switch tools.

Push Atlas hooks through managed settings or the MDM you already use. No per-machine setup.
Push Atlas hooks through managed settings or the MDM you already use. No per-machine setup.

Policies run in your own data plane. No unencrypted LLM data leaves your account.
Policies run in your own data plane. No unencrypted LLM data leaves your account.

Focus on the permissions and exposed data that could increase the impact of a breach.
Bring data discovery, access visibility, and activity monitoring together to support your compliance program.
Runtime protection
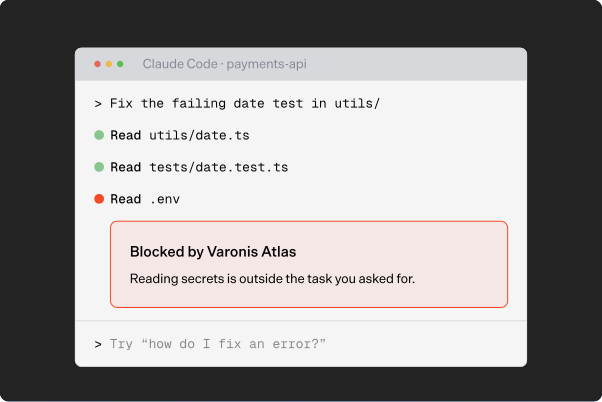
Atlas checks each prompt, tool call, file read, and response as it happens. Block, modify, alert, or log. Intent-based access control catches actions that are allowed but outside the task.
Visibility
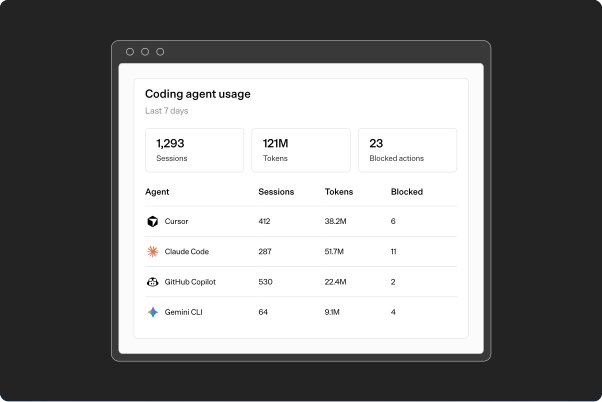
See who used which agent, what they asked, and every tool and MCP server the agent called. Replay any session with the policy decisions applied. Track usage and token spend by user, team, and project.
Posture
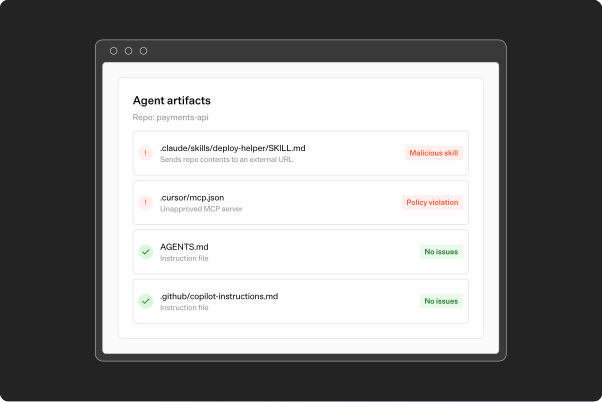
Atlas finds the skills, memory, instruction files, and MCP configurations in your repositories. Posture policies flag the risky ones, including malicious skills.
Threat detection
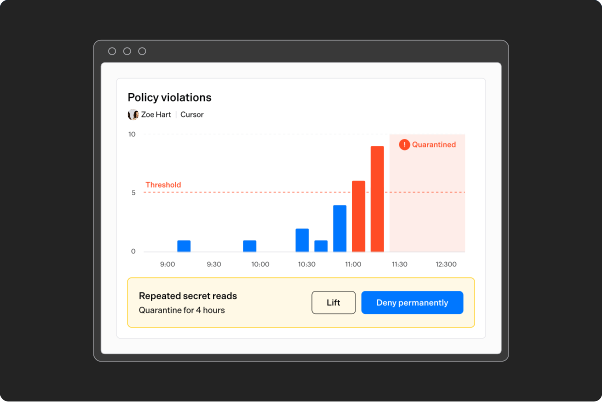
Atlas spots repeated violations and suspicious tool or MCP use across a session. Quarantine the user for a set time, or deny them permanently. Trusted developers keep their agents.
FAQs

Cursor, Claude Code, VS Code, GitHub Copilot, OpenAI Codex, Kiro, Devin, Google Antigravity, and Gemini CLI.
No. Atlas is an independent layer. It enforces the same policy no matter which agent or model a developer uses.
Endpoint tools see processes and files. Atlas sees what the developer asked for and what the agent did next. It checks whether each action fits the task.
No. Artifact discovery runs separately from the hooks.
Yes. It logs every MCP server call and flags suspicious MCP use. It also finds MCP configurations in your repos.

