Monitor every database
Protect SQL Server, Oracle, PostgreSQL, MySQL, MongoDB, Snowflake, Databricks, and more from one console.
Protect SQL Server, Oracle, PostgreSQL, MySQL, MongoDB, Snowflake, Databricks, and more from one console.
DATABASE ACTIVITY MONITORING
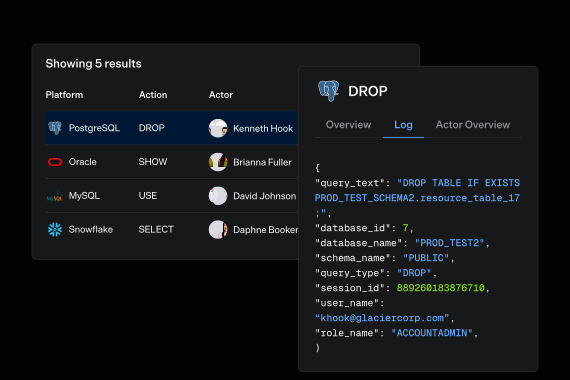
Legacy DAM puts agents on every server and appliances in every data center. Varonis is cloud-native, simple to deploy, and gives you true database security, not just logs for compliance.
Trusted by 8,000+ customers




WHY VARONIS DAM
Tools like Imperva and IBM Guardium need software on every database server, constant tuning, and a team to run them. So teams watch a few critical databases and hope for the best on the rest. Varonis covers the whole estate from one cloud-native platform.
Protect SQL Server, Oracle, PostgreSQL, MySQL, MongoDB, Snowflake, Databricks, and more from one console.
Protect SQL Server, Oracle, PostgreSQL, MySQL, MongoDB, Snowflake, Databricks, and more from one console.

AI classification finds sensitive data. Threat detection flags abnormal queries. Inline blocking stops them.
AI classification finds sensitive data. Threat detection flags abnormal queries. Inline blocking stops them.

Revoke excessive permissions, remove stale access, and block risky sessions before they reach sensitive data.
Revoke excessive permissions, remove stale access, and block risky sessions before they reach sensitive data.

Focus on the permissions and exposed data that could increase the impact of a breach.
Bring data discovery, access visibility, and activity monitoring together to support your compliance program.
Your newest database users are AI agents
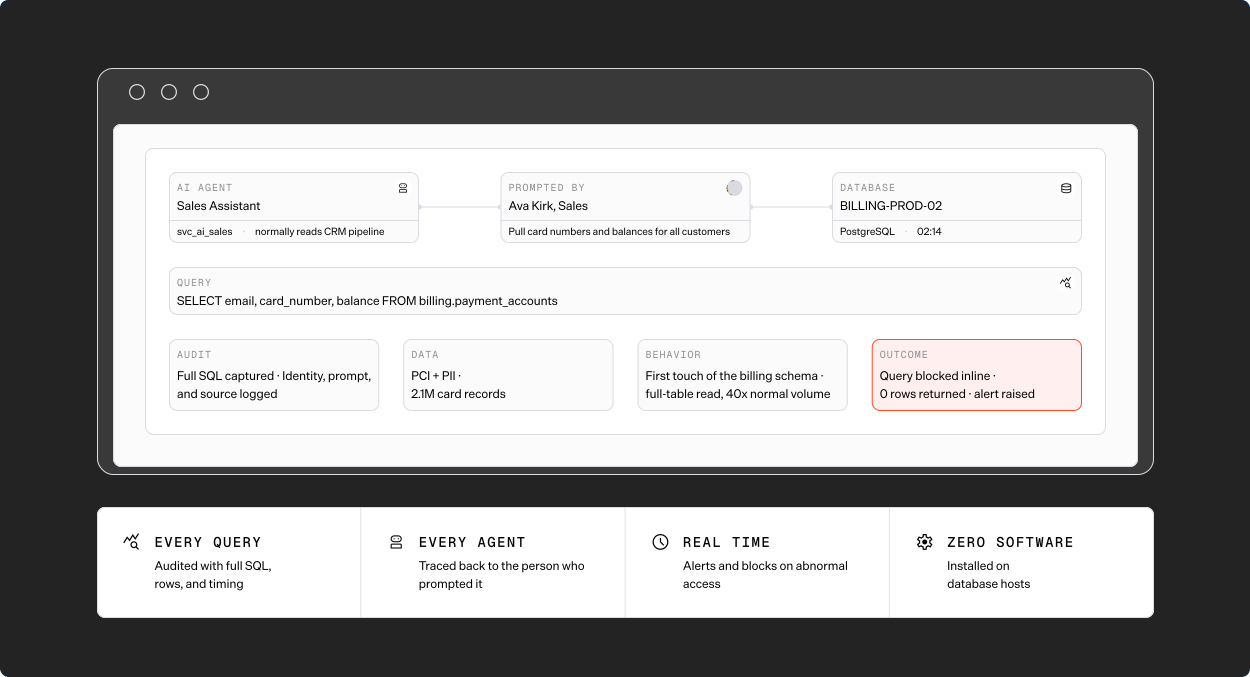
Agents run under shared service accounts, at machine speed, with more access than any person would get. Varonis audits every query they run, ties it back to the person who prompted it, and alerts on or blocks anything abnormal before data leaves.
Real-time prevention
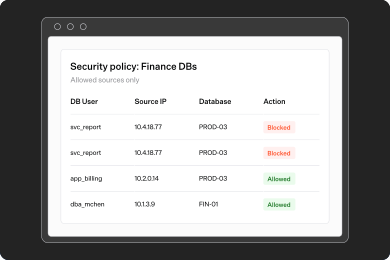
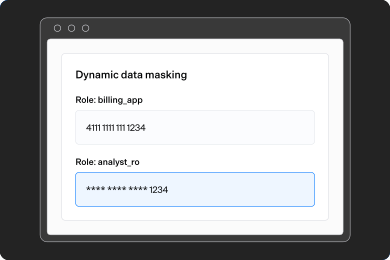
Block disallowed sessions, mask sensitive fields by role, and tie every login to a real person. Every action is logged for the audit and the investigation.
Enforce policies on SQL Server, Oracle, PostgreSQL, MySQL, MongoDB, and Db2. Nothing changes on the database engine.
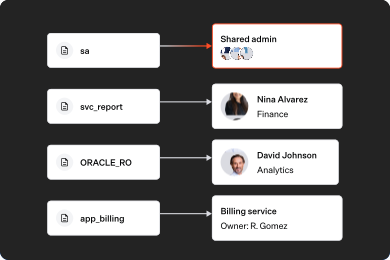
Varonis maps database accounts and service accounts to real people in Active Directory and Entra ID. Shared credentials stop hiding who did what.
Dynamic masking hides card numbers and other sensitive fields from roles that don't need them. Applications keep working.
"It’s not just a tool, it’s a relationship. We always feel Varonis is there for us, and they’ve never wavered. That’s why I love Varonis."
Brian Valiquette
Director of Information Security Risk & Compliance
"Leveraging Varonis to properly permission our files gives me the confidence to move forward with AI adoption."

Jacob Lorz
VP Information Technology & CISO

“The only reason I'm prepared and feel safe in recommending our AI products through AI Governance Committee is because we have Varonis.”

Jim Bowie
CISO

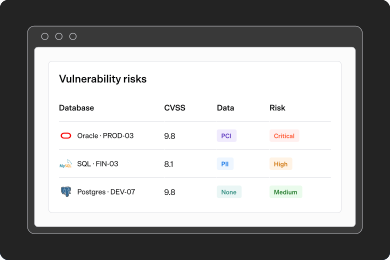
Every database is checked against published CVEs for its exact version. Findings are ranked by the data at stake, so a CVE on a PCI database jumps the queue.
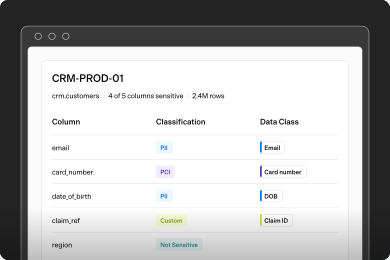
AI classification scans tables, columns, and rows for PII, PCI, PHI, and secrets, plus data types unique to your business. No regex rules to write or tune.
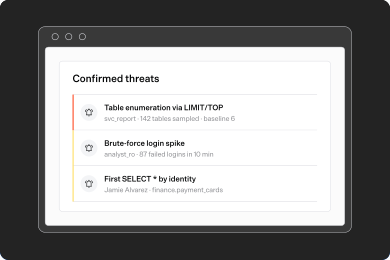
Varonis learns each identity's normal database activity. It flags table enumeration, brute-force logins, and first-time SELECT * queries before data leaves.
PROOF
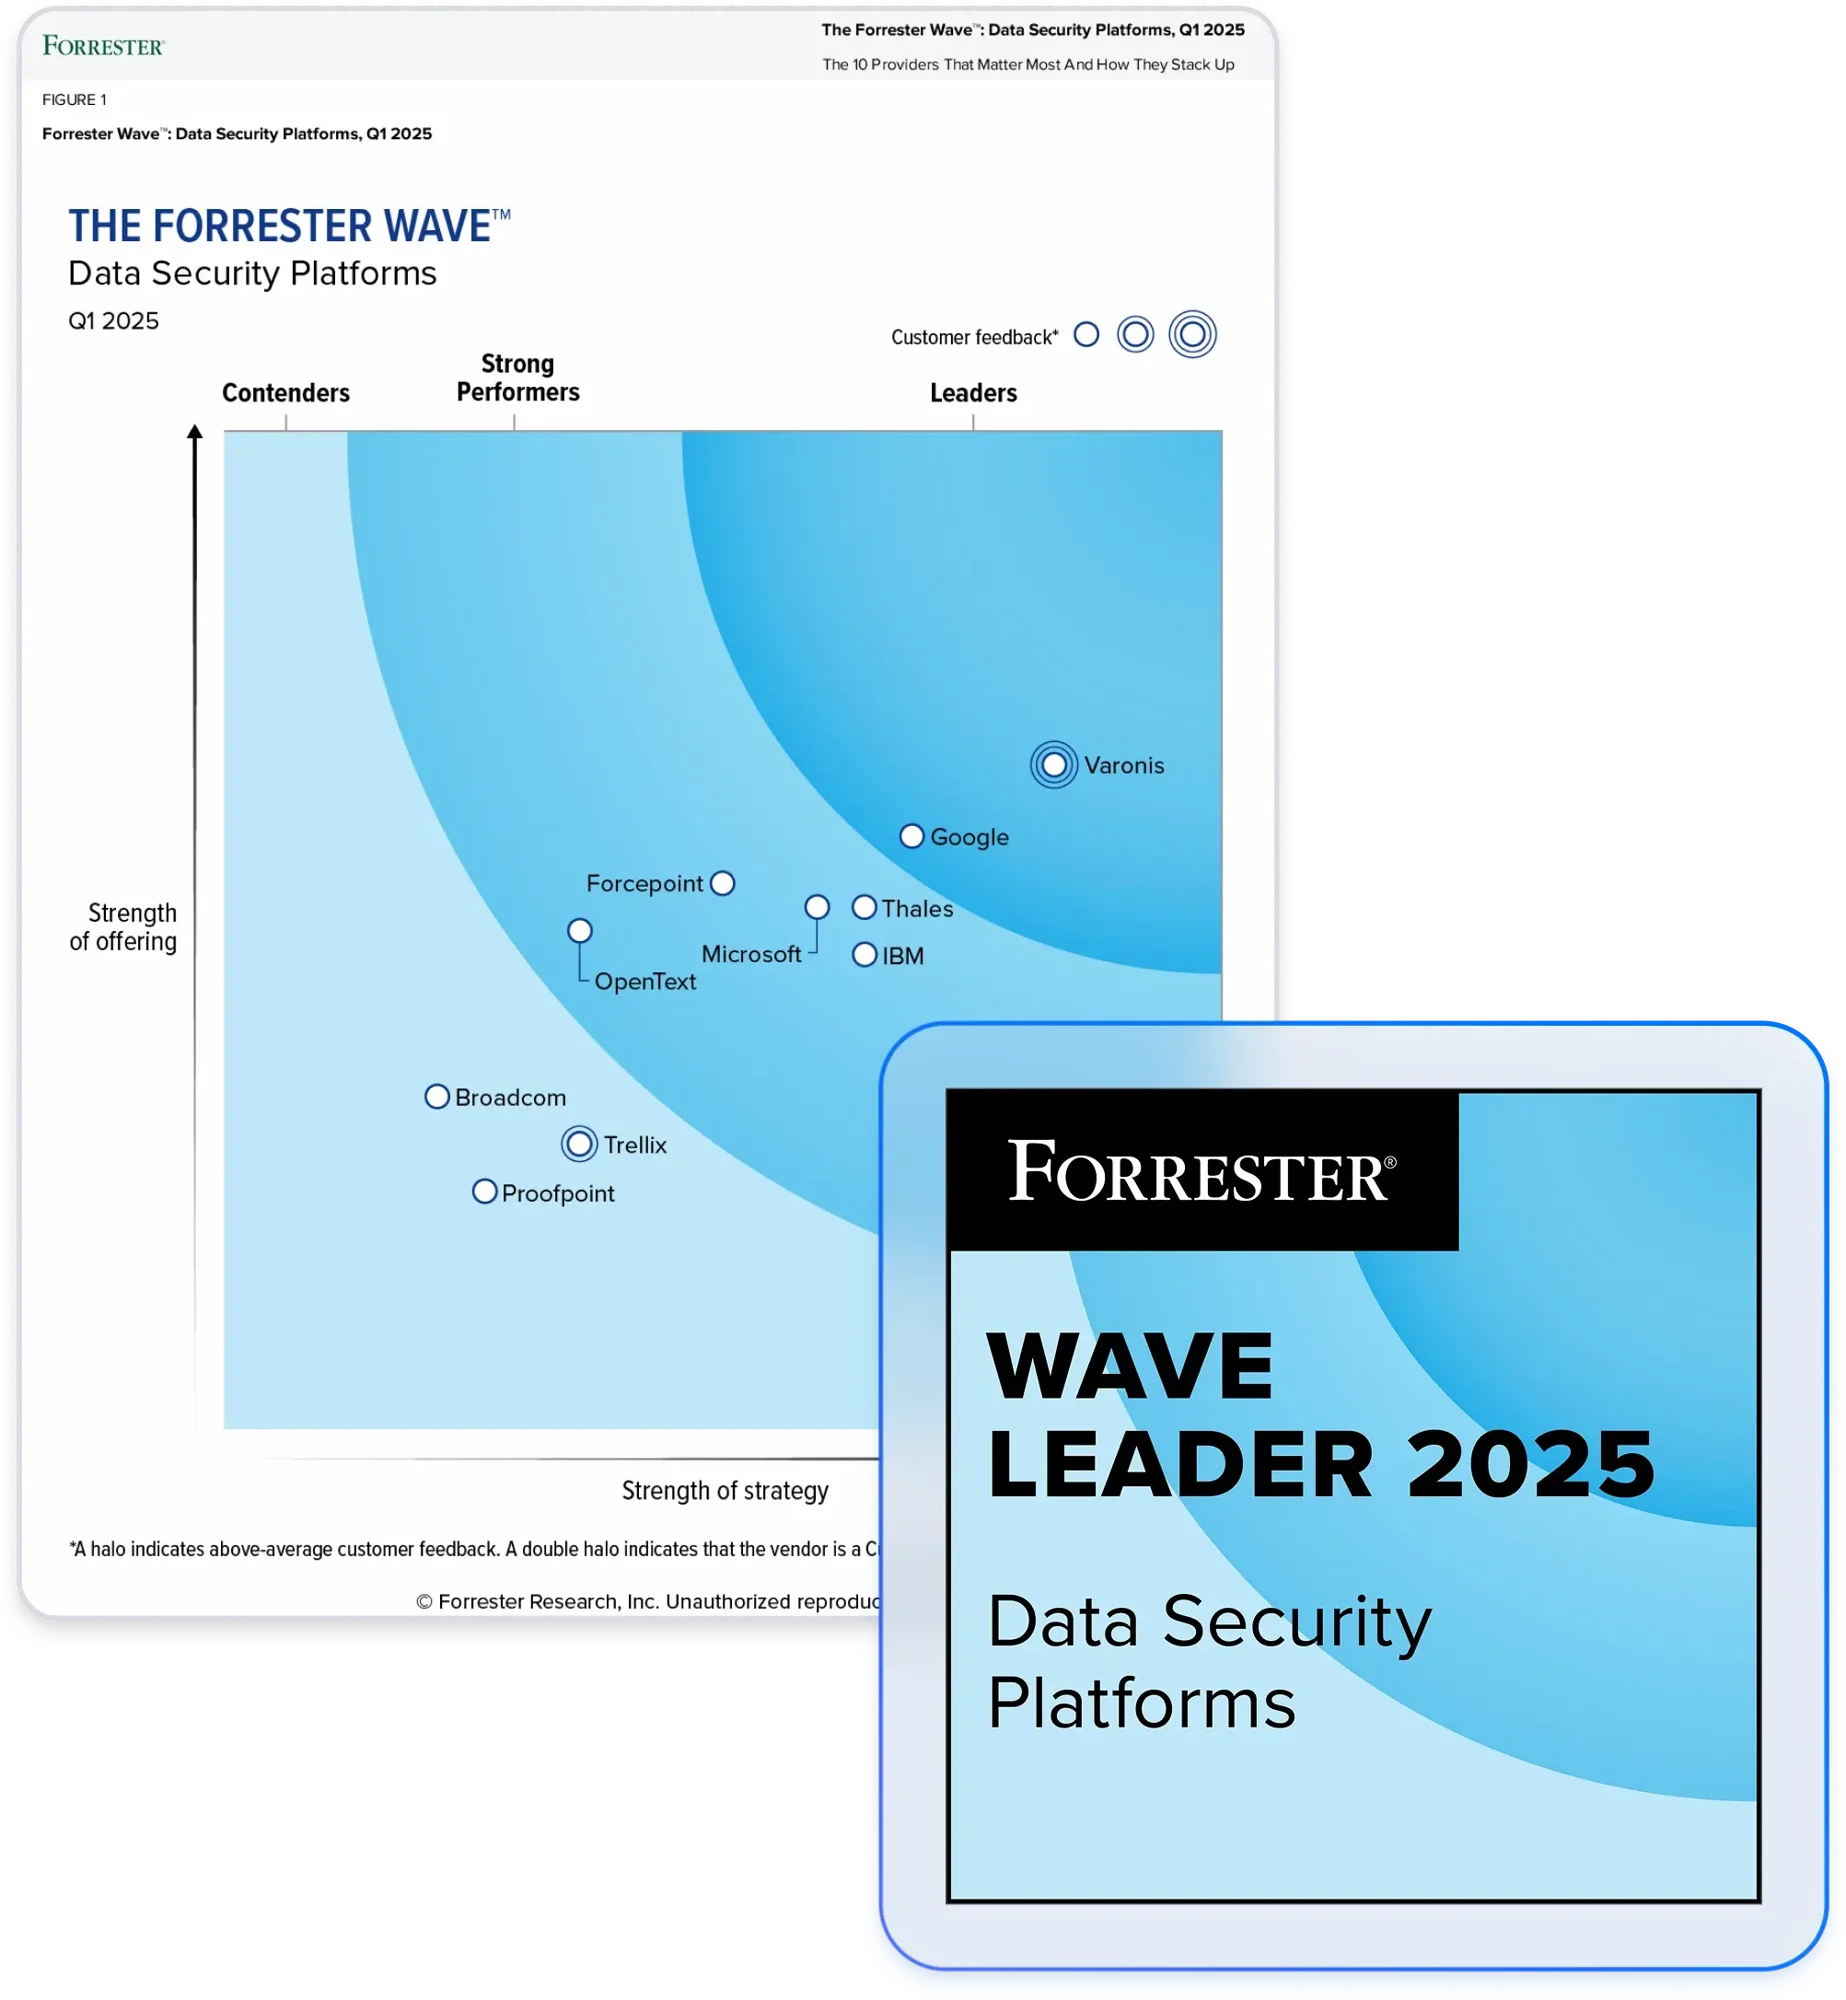
Security teams choose Varonis to find and stop data breaches. See what they say on G2 and why Forrester named us a Leader.



FEATURED RESOURCES
Learn why legacy DAM and SIEM leave your databases exposed.
Go beyond DAM
Extend the platform to every place your data lives and moves.
FAQS

DAM tracks every query against your databases. It shows who accessed sensitive data, what they did, and whether it broke policy. Varonis adds data classification, identity, and behavior so you can stop threats, not just record them.
We cover virtually every major database flavor, including: SQL Server, Oracle, PostgreSQL, MySQL, MongoDB, Db2, Snowflake, Databricks, Amazon RDS, and cloud databases in AWS, Azure, and Google Cloud. You can find our full coverage list here.
No. Varonis collects native audit logs through a lightweight collector, with under 5% overhead. For your most critical databases, the Gatekeeper adds inline blocking. Neither installs anything on the database host.
Either, and many databases support both. Native auditing uses the logs your database already produces, with nothing in the data path. The Gatekeeper sits inline next to the database and adds real-time blocking and masking. The right fit depends mostly on the native audit capabilities of each database engine, and you can mix both across your estate.
A SIEM charges you to store raw logs but doesn't know which tables hold regulated data or who is really behind a service account. Varonis turns those logs into findings with data and identity context.
Both rely on agents, appliances, and long rollouts, so most databases go unmonitored. Varonis is cloud-native, deploys in weeks, fixes risk automatically, and comes with 24x7 MDDR.
Yes. Set policies by database user, source IP, or both. The Gatekeeper evaluates each connection in real time and refuses disallowed sessions before any query runs.
Yes. Vulnerability findings, remediation history, and activity records export as timestamped evidence. Varonis maps your data to frameworks like PCI DSS, HIPAA, and GDPR.
Setup takes under an hour, and findings show up within 24 hours. You get a data map, identity mapping, live alerts watched by an MDDR analyst, and an executive report with next steps.