-
Nov 15, 2022
Varonis Threat Labs Discovers SQLi and Access Flaws in Zendesk
Varonis Threat Labs found a SQL injection vulnerability and a logical access flaw in Zendesk Explore, the reporting and analytics service in the popular customer service solution, Zendesk.
Tal Peleg
3 min read
-
Oct 25, 2022
The Logging Dead: Two Event Log Vulnerabilities Haunting Windows
You don’t have to use Internet Explorer for its legacy to have left you vulnerable to LogCrusher and OverLog, a pair of Windows vulnerabilities discovered by the Varonis Threat Labs team.
Dolev Taler
4 min read
-

Sep 15, 2022
Fighting Golden Ticket Attacks with Privileged Attribute Certificate (PAC)
Learn how and why to control the Active Directory Environment state with PACRequestorEnforcement, the implications of doing so and how to detect Golden Ticket attacks happening in your network.
Masha Garmiza
4 min read
-
Aug 22, 2022
Anatomy of a SolidBit Ransomware Attack
Solidbit is a ransomware variant derived from Yashma and containing elements of LockBit. Discover how Solidbit's capabilities, execution, what file types it targets, and how to tell if you're been infected.
Jason Hill
6 min read
-
Jun 17, 2022
Anatomy of a LockBit Ransomware Attack
A detailed case study of the exact techniques and methods that threat actors used in a real-life ransomware attack.
Joseph Avanzato
8 min read
-
Jun 16, 2022
Rogue Shortcuts: LNK'ing to Badness
Learn how threat actors continue to manipulate Windows shortcut files (LNKs) as an exploit technique.
Jason Hill
5 min read
-
May 11, 2022
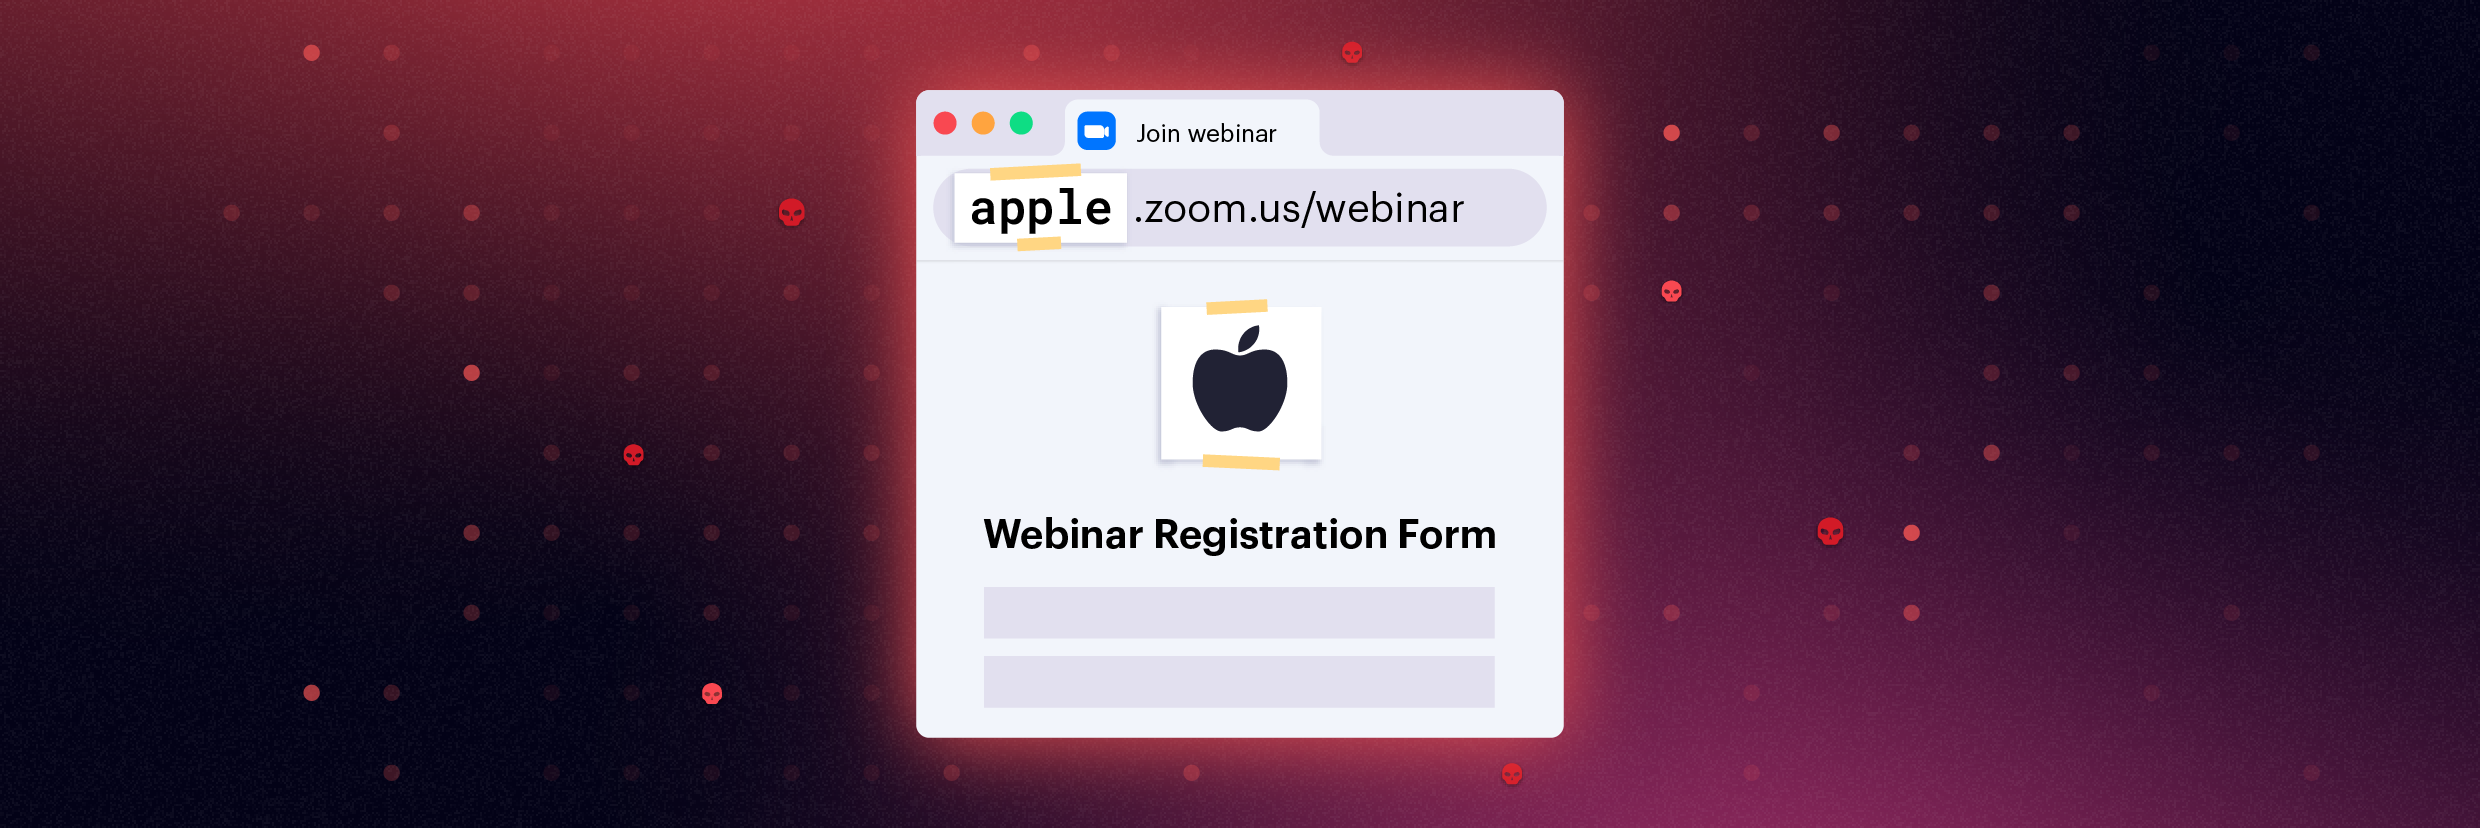
Spoofing SaaS Vanity URLs for Social Engineering Attacks
SaaS vanity URLs can be spoofed and used for phishing campaigns and other attacks. In this article, we’ll showcase two Box link types, two Zoom link types, and two Google Docs link type that we were able to spoof.
Tal Peleg
6 min read
-
Apr 19, 2022
Hive Ransomware Analysis
Learn how Hive ransomware exploits public servers, spreads through your network, encrypts sensitive files, and exports victims for cryptocurrency.
Nadav Ovadia
7 min read
-
Mar 29, 2022
Defending Your Cloud Environment Against LAPSUS$-style Threats
Varonis breaks down the recent LAPSUS$ hacks and provides best practices for defending your cloud environment against LAPSUS$ style threats
Nathan Coppinger
6 min read
-
Mar 11, 2022
Is this SID taken? Varonis Threat Labs Discovers Synthetic SID Injection Attack
A technique where threat actors with existing high privileges can inject synthetic SIDs into an ACL creating backdoors and hidden permission grants.
Eric Saraga
3 min read
-
Mar 04, 2022
ContiLeaks: Ransomware Gang Suffers Data Breach
Conti, a prolific ransomware group, has suffered a leak of both internal chat transcripts and source code being shared by a reported Ukrainian member
Jason Hill
6 min read
-
Feb 03, 2022
Ransomware Year in Review 2021
In this post, we dive into six ransomware trends that shaped 2021.
Varonis Threat Labs
10 min read