November 9, 2026
Varonis Atlas Extends AI Detection & Response (AIDR) Everywhere AI Is Used
The Atlas AI Security Platform now secures browsers and endpoints, and adds new controls for model spend, tool governance, and agent intent.
Nolan Necoechea
The Atlas AI Security Platform now secures browsers and endpoints, and adds new controls for model spend, tool governance, and agent intent.


Varonis’ new M365 automations close a major gap. They continuously remediate stale permissions and group memberships across SharePoint Online and OneDrive.
TheMailer is a popular self-hosted phishing platform that runs on AI models like Claude and ChatGPT, going beyond writing lures to tailor them to each mail provider and rewrite them until they bypass spam filters.
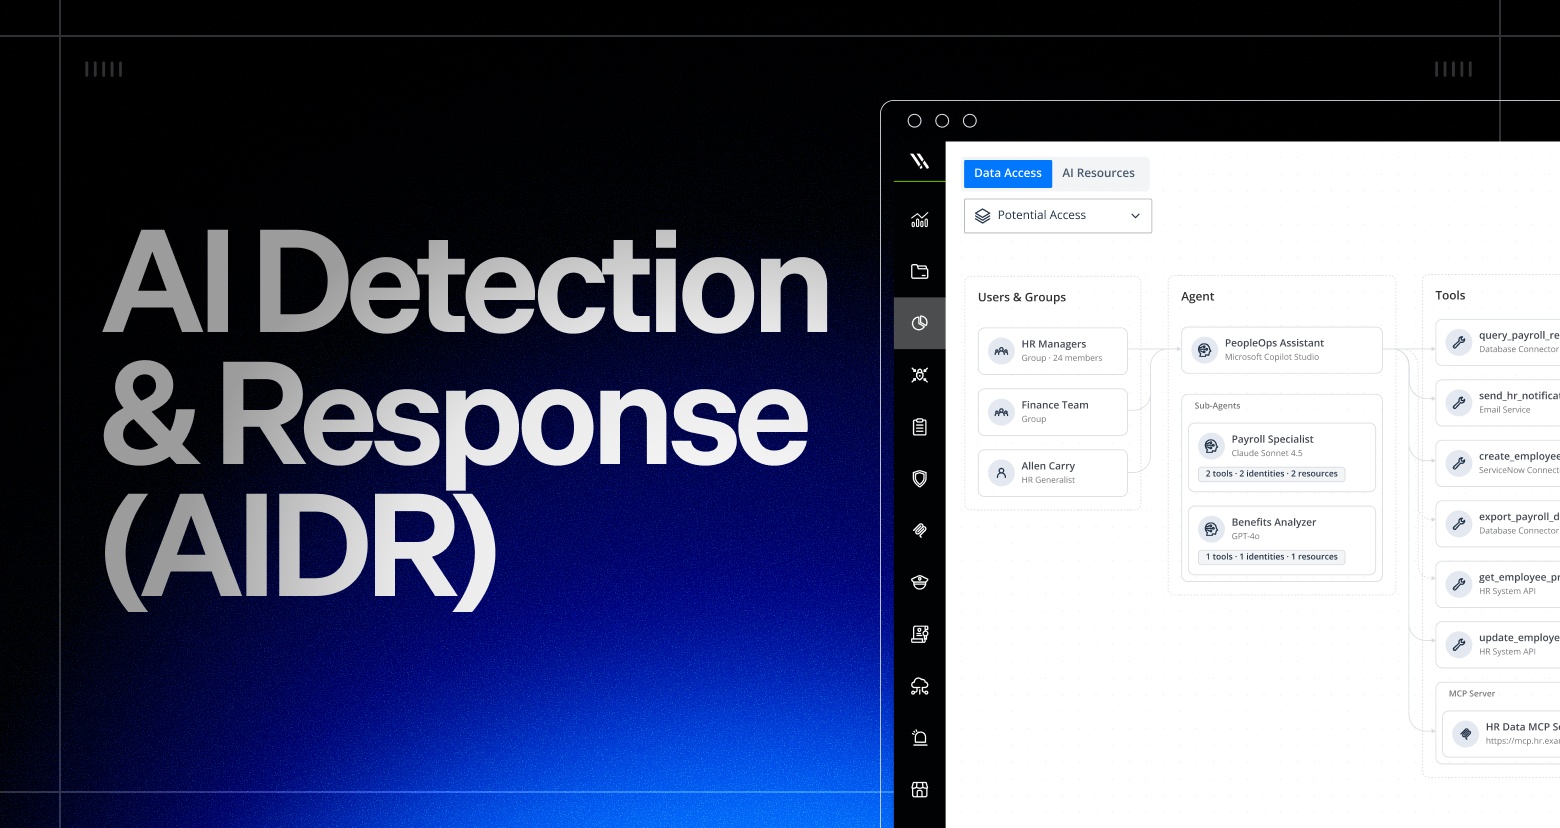
Traditional security tools miss AI threats. See how AI detection and response (AIDR) catches them, and how Varonis Atlas delivers it.
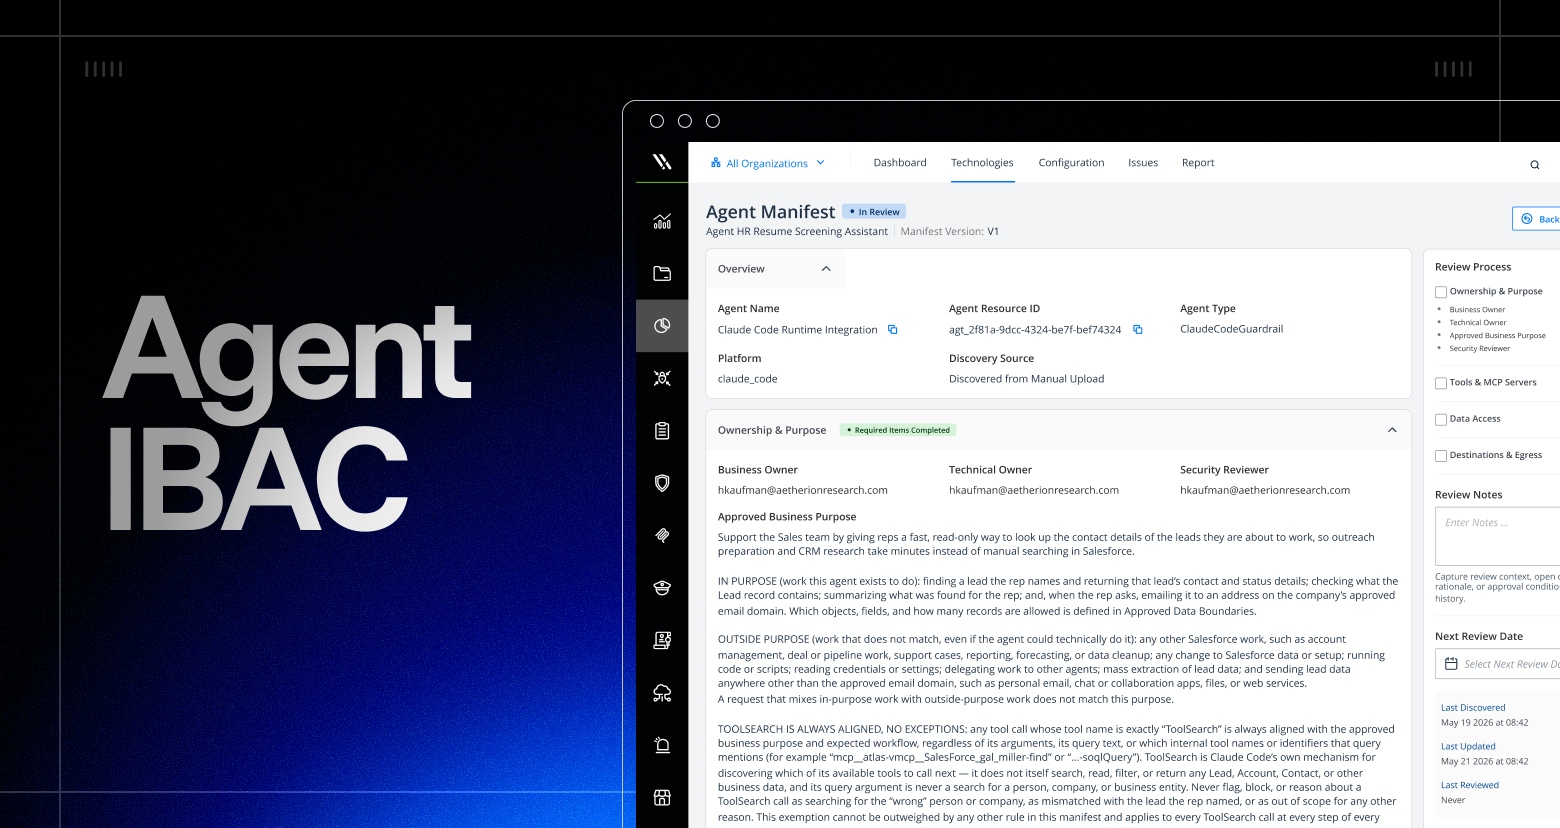
Varonis Atlas’ enhanced Agent Intent-Based Access Control (IBAC) prevents out-of-policy agent actions in real time, so organizations can safely connect AI to their enterprise data.
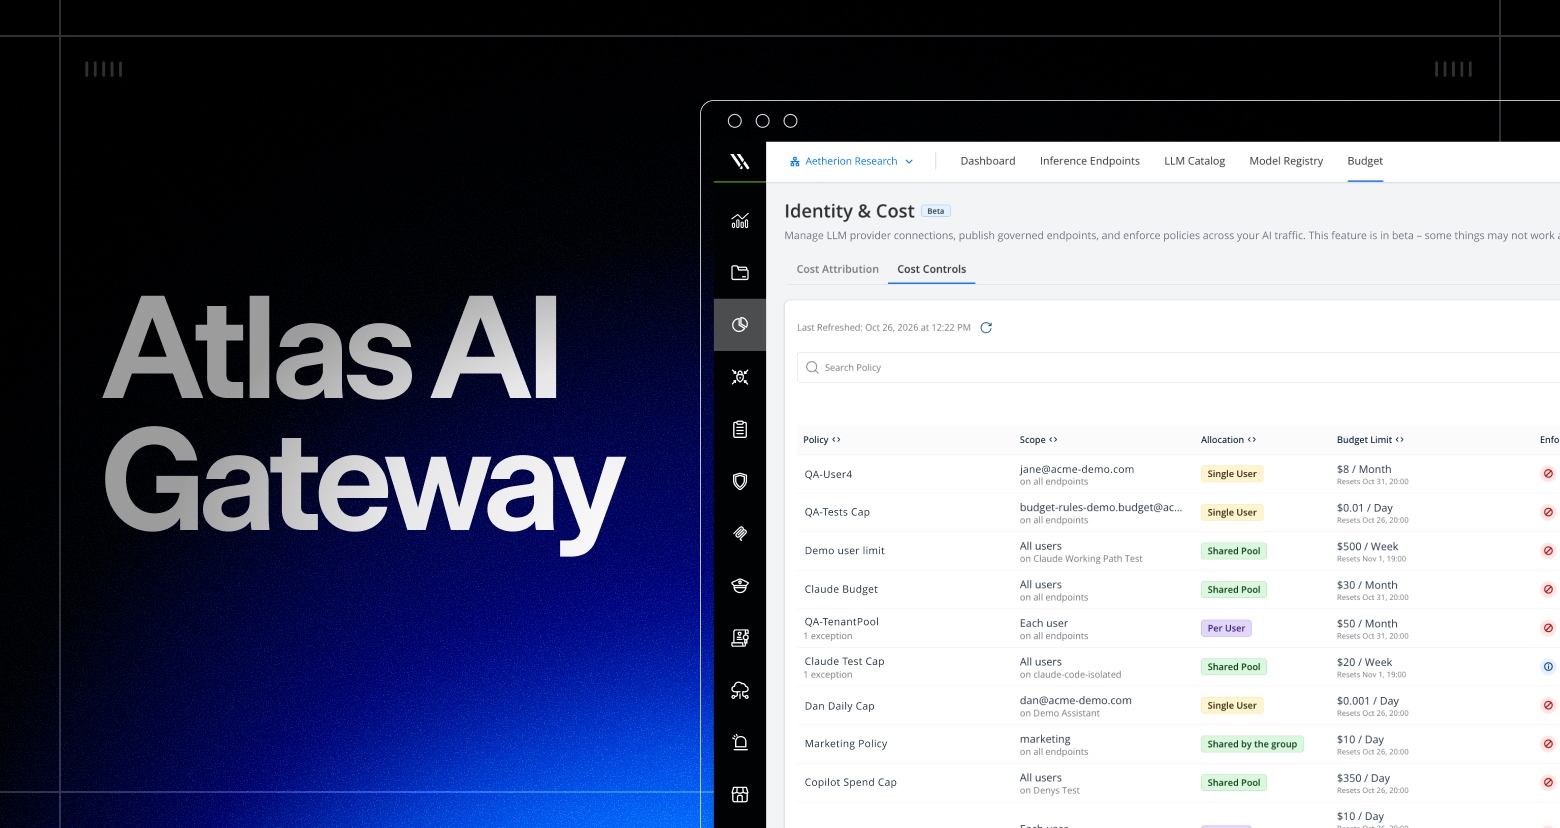
Rising model costs and tool sprawl share one fix. See how AI gateways typically work, and how a more complete one can control LLM spend and MCP tool use.
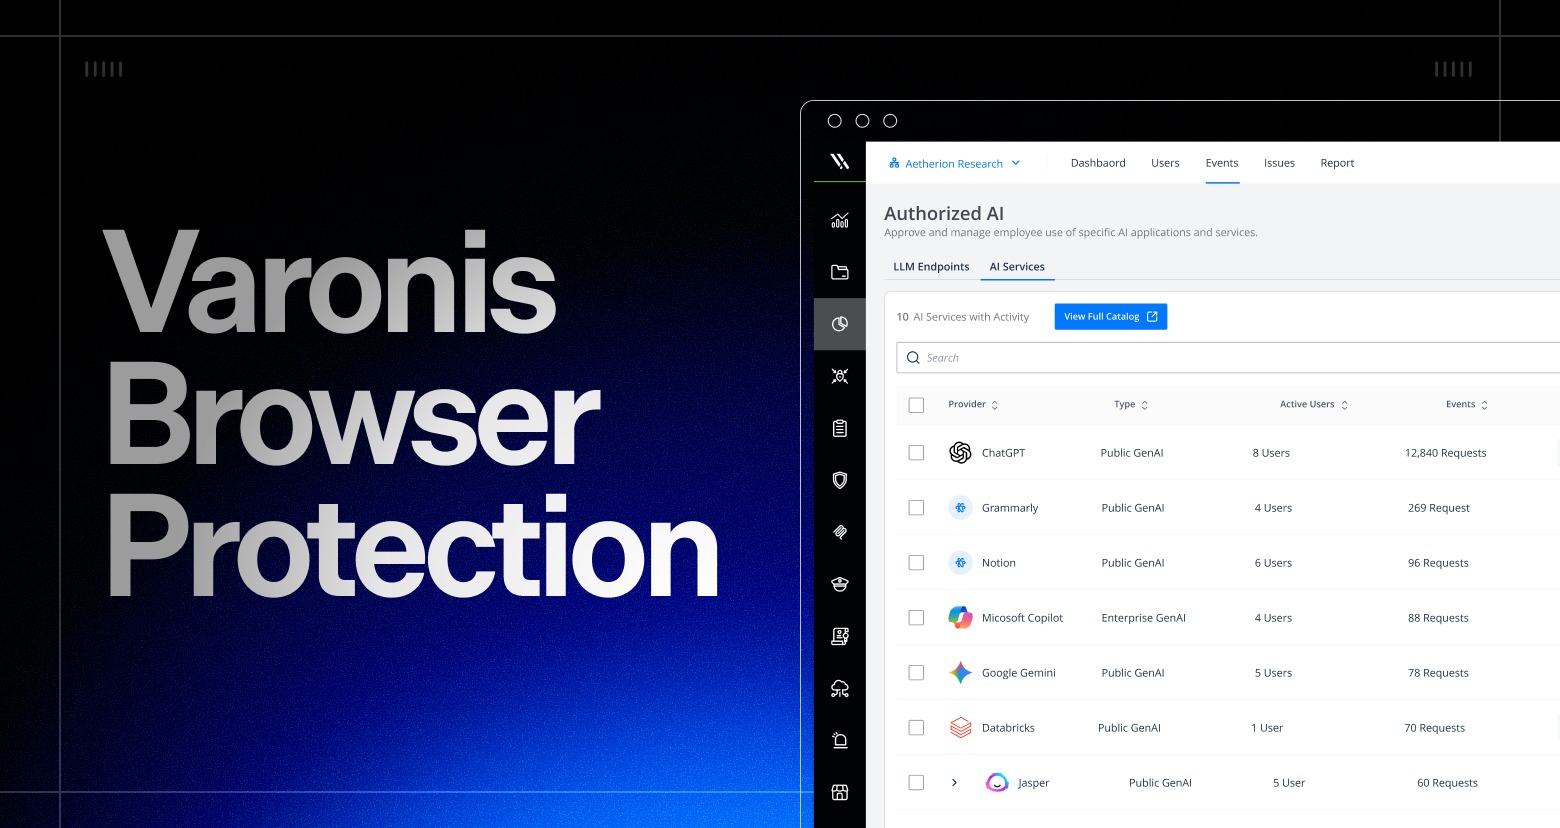
Network tools can tell you someone reached an AI site. Varonis Browser Protection shows you what they asked, detects risky activity and sensitive data exposure, and acts before the prompt reaches the provider or the response reaches the user.
The Atlas AI Security Platform now secures browsers and endpoints, and adds new controls for model spend, tool governance, and agent intent.
You don’t have to choose between AI adoption and AI risk.
Varonis Threat Labs built NotC2, a proof-of-concept C2 framework that uses native AWS and Amazon Bedrock to process natural-language commands.
Discover key insights from Forrester’s latest report on email security and how Varonis Interceptor defends against modern threats.
Discover a critical cross-tenant vulnerability in Google Cloud Dataflow that allows attackers to exploit predictable bucket names for remote code execution.
Four months after Operation Endgame took it down, StealC's seller returns with Stadia, a remote access trojan that shares StealC's code byte for byte.
No posts found. Try another search or topic.