What's new
Explore our latest product enhancements, release notes, acquisitions, and more.
October 07, 2026
AI classification scope controls
Platform (Data Security)
October 04, 2026
Automate sensitive data masking in Databricks
Platform (Data Security)
October 04, 2026
Track Snowflake database sizes for capacity planning and reporting
Platform (Data Security)
Oct 2026
Oct 07, 2026
Oct 07, 2026
Platform (Data Security)
AI classification scope controls
Control the scope of LLM-based classification by selecting specific services and accounts for AI processing. Scoped configurations ensure only designated repositories are included in structured, semi-structured, and unstructured AI classification workflows, helping align AI processing with business, compliance, operational, and cost-management requirements.
Oct 04, 2026
Oct 04, 2026
Platform (Data Security)
Improved database capacity planning and reporting
Export scoped database instance information, including instance sizes in raw bytes and human-readable MB/GB units, directly to CSV. Accessible database sizing information supports capacity planning and reporting without requiring manual collection or external tools.
Oct 04, 2026
Oct 04, 2026
Platform (Data Security)
Track Snowflake database sizes for capacity planning and reporting
View Snowflake database sizes directly in Varonis to support capacity planning, sizing, and reporting. Database size metadata is available in Investigation views and can be exported to CSV in both raw bytes and human-readable MB/GB units.
Oct 04, 2026
Oct 04, 2026
Platform (Data Security)
Apply Data Concentration to database classification
Varonis now applies Data Concentration to database tables to reduce repetitive classification across tables with matching structures. Varonis groups tables with the same schema and classifies up to 10 representative tables per group.
Oct 04, 2026
Oct 04, 2026
Platform (Data Security)
Automate sensitive data masking in Databricks
Automate Databricks column-level data masking directly from Varonis. By synchronizing each column’s effective masking state and tagging columns as masked or unmasked, Varonis gives customers a centralized view of masking coverage. Masking can be enabled or disabled directly from policy automation workflows, streamlining remediation and improving visibility into sensitive data exposure.
Sep 2026
Sep 16, 2026
Sep 16, 2026
Platform (Data Security)
Prioritize collector capacity based on scanning needs
Control how local collector processing capacity is allocated between initial discovery and incremental scans. Configurable scan ratios can prioritize faster initial scan completion or allocate more capacity to incremental scans in environments with high data activity, with a balanced 50/50 allocation used by default.
Sep 16, 2026
Sep 16, 2026
Platform (Data Security)
Simplify deployment of container repositories
Configure private container repositories directly from the collector deployment UI. Repository details are automatically incorporated into the generated Helm chart, eliminating manual repository configuration and simplifying deployments that rely on private container registries.
Sep 15, 2026
Sep 15, 2026
Platform (Data Security)
Data Lifecycle Management
Cut storage costs, improve AI outputs, and reduce risk with Data Lifecycle Management
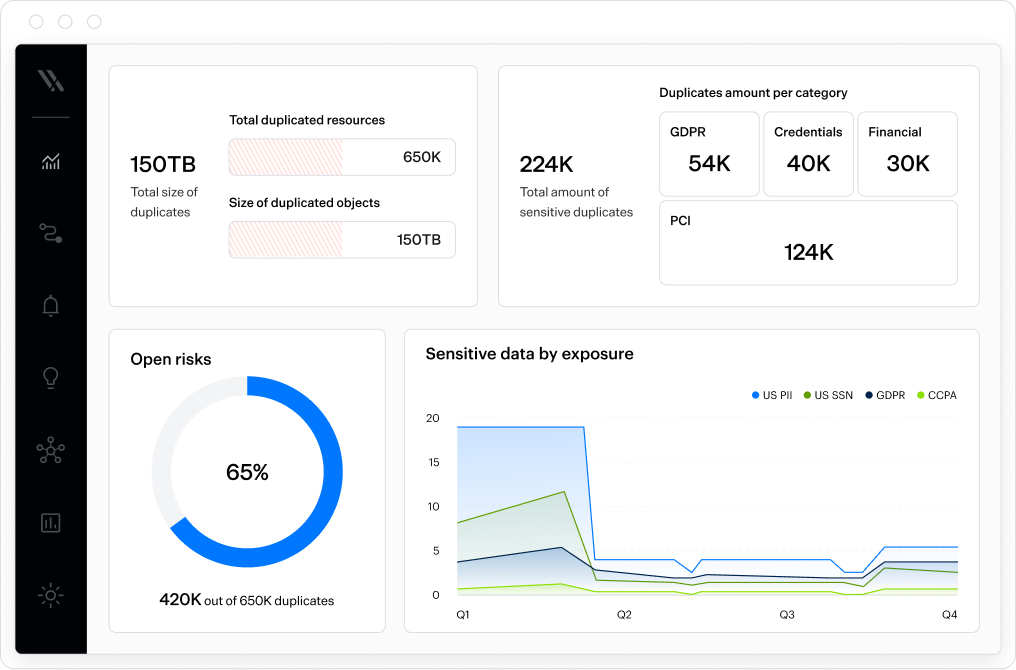
Varonis Data Lifecycle Management (DLM) automatically identifies, prioritizes, and quarantines redundant, obsolete, and trivial (ROT) data across connected data sources. Powered by the Varonis Data Security Platform, DLM combines data classification, permissions mapping, and activity analysis to identify stale, duplicate, overexposed, and expired data. By reducing the volume of unnecessary data stored across the enterprise, DLM helps lower storage and backup costs, minimize security and compliance risk, and maintain cleaner data for AI-driven workflows and analytics.
Learn more about DLM here.
Learn more about DLM here.
Sep 15, 2026
Sep 15, 2026
Platform (Data Security)
Migrate Salesforce integrations to Salesforce's External Client App framework
Migrate existing Salesforce integrations to Salesforce’s External Client app framework. This one-time migration preserves existing integration configurations and aligns with Salesforce Security recommendations and the AppExchange distribution model. No end-user action is required after migration.
Sep 09, 2026
Sep 09, 2026
Platform (Data Security)
Bring your own secret manager
Configure Private Cloud Data Collectors to use AWS Secrets Manager, Azure Key Vault, or HashiCorp Vault for secret storage. Customer-managed secret stores centralize credential management, extend existing access controls, and align collector credential storage with established security and compliance requirements.
Sep 07, 2026
Sep 07, 2026
Platform (Data Security)
Investigate Confluence page history
Analyze historical versions of Confluence pages to uncover sensitive content across page history. Pages containing sensitive data in historical versions are automatically tagged to support investigation and remediation workflows.
Sep 07, 2026
Sep 07, 2026
Platform (Data Security)
Customize on-demand scan prioritization
Select either a Prioritized Scan for faster access to updated results or a standard queued rescan when immediate execution is not required. Flexible scan scheduling helps balance scan urgency with efficient use of scanning resources.